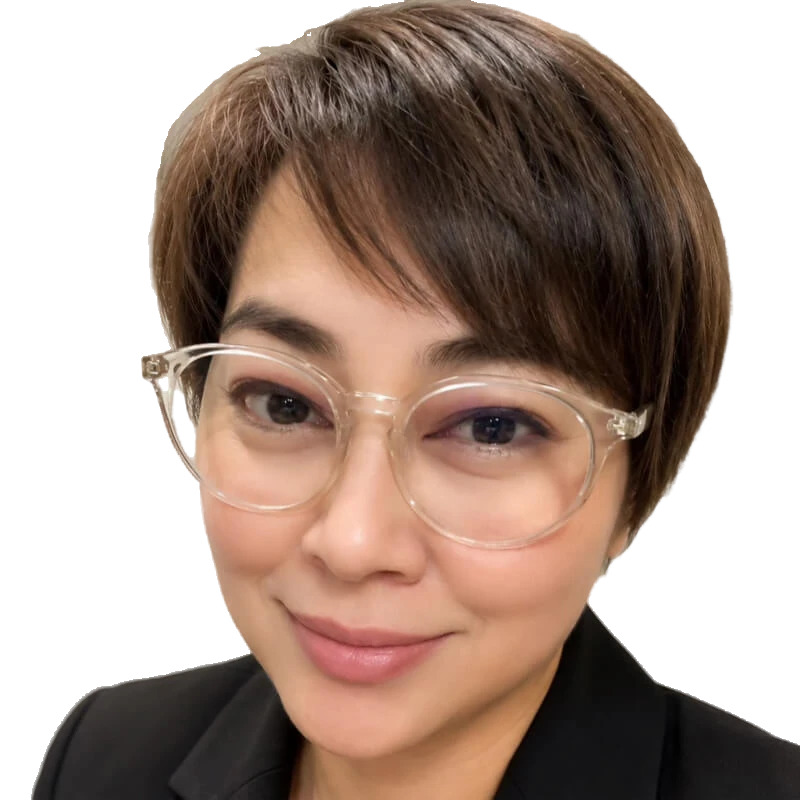
Guarding personal data across a telecommunications network serving tens of millions of subscribers requires more than managing scale. It requires navigating rapid, organization-wide transformation while ensuring that privacy, cybersecurity, governance, and risk management remain embedded in how an enterprise operates. One privacy leader demonstrates how trust can become the foundation for both resilience and responsible innovation.
As the Asia-Pacific Data Privacy Organization (APDPO) continues its Leading with Privacy series, it spotlights Leah Besa-Jimenez, PLDT Group Chief Data Privacy Officer and the 2026 Cyber Woman of the Year. In a discussion with Magie Antonio, APDPO Country Head for the Philippines, Besa-Jimenez shared her insights on privacy, trust, institutional resilience, and the responsibility that comes with handling the personal data of millions.
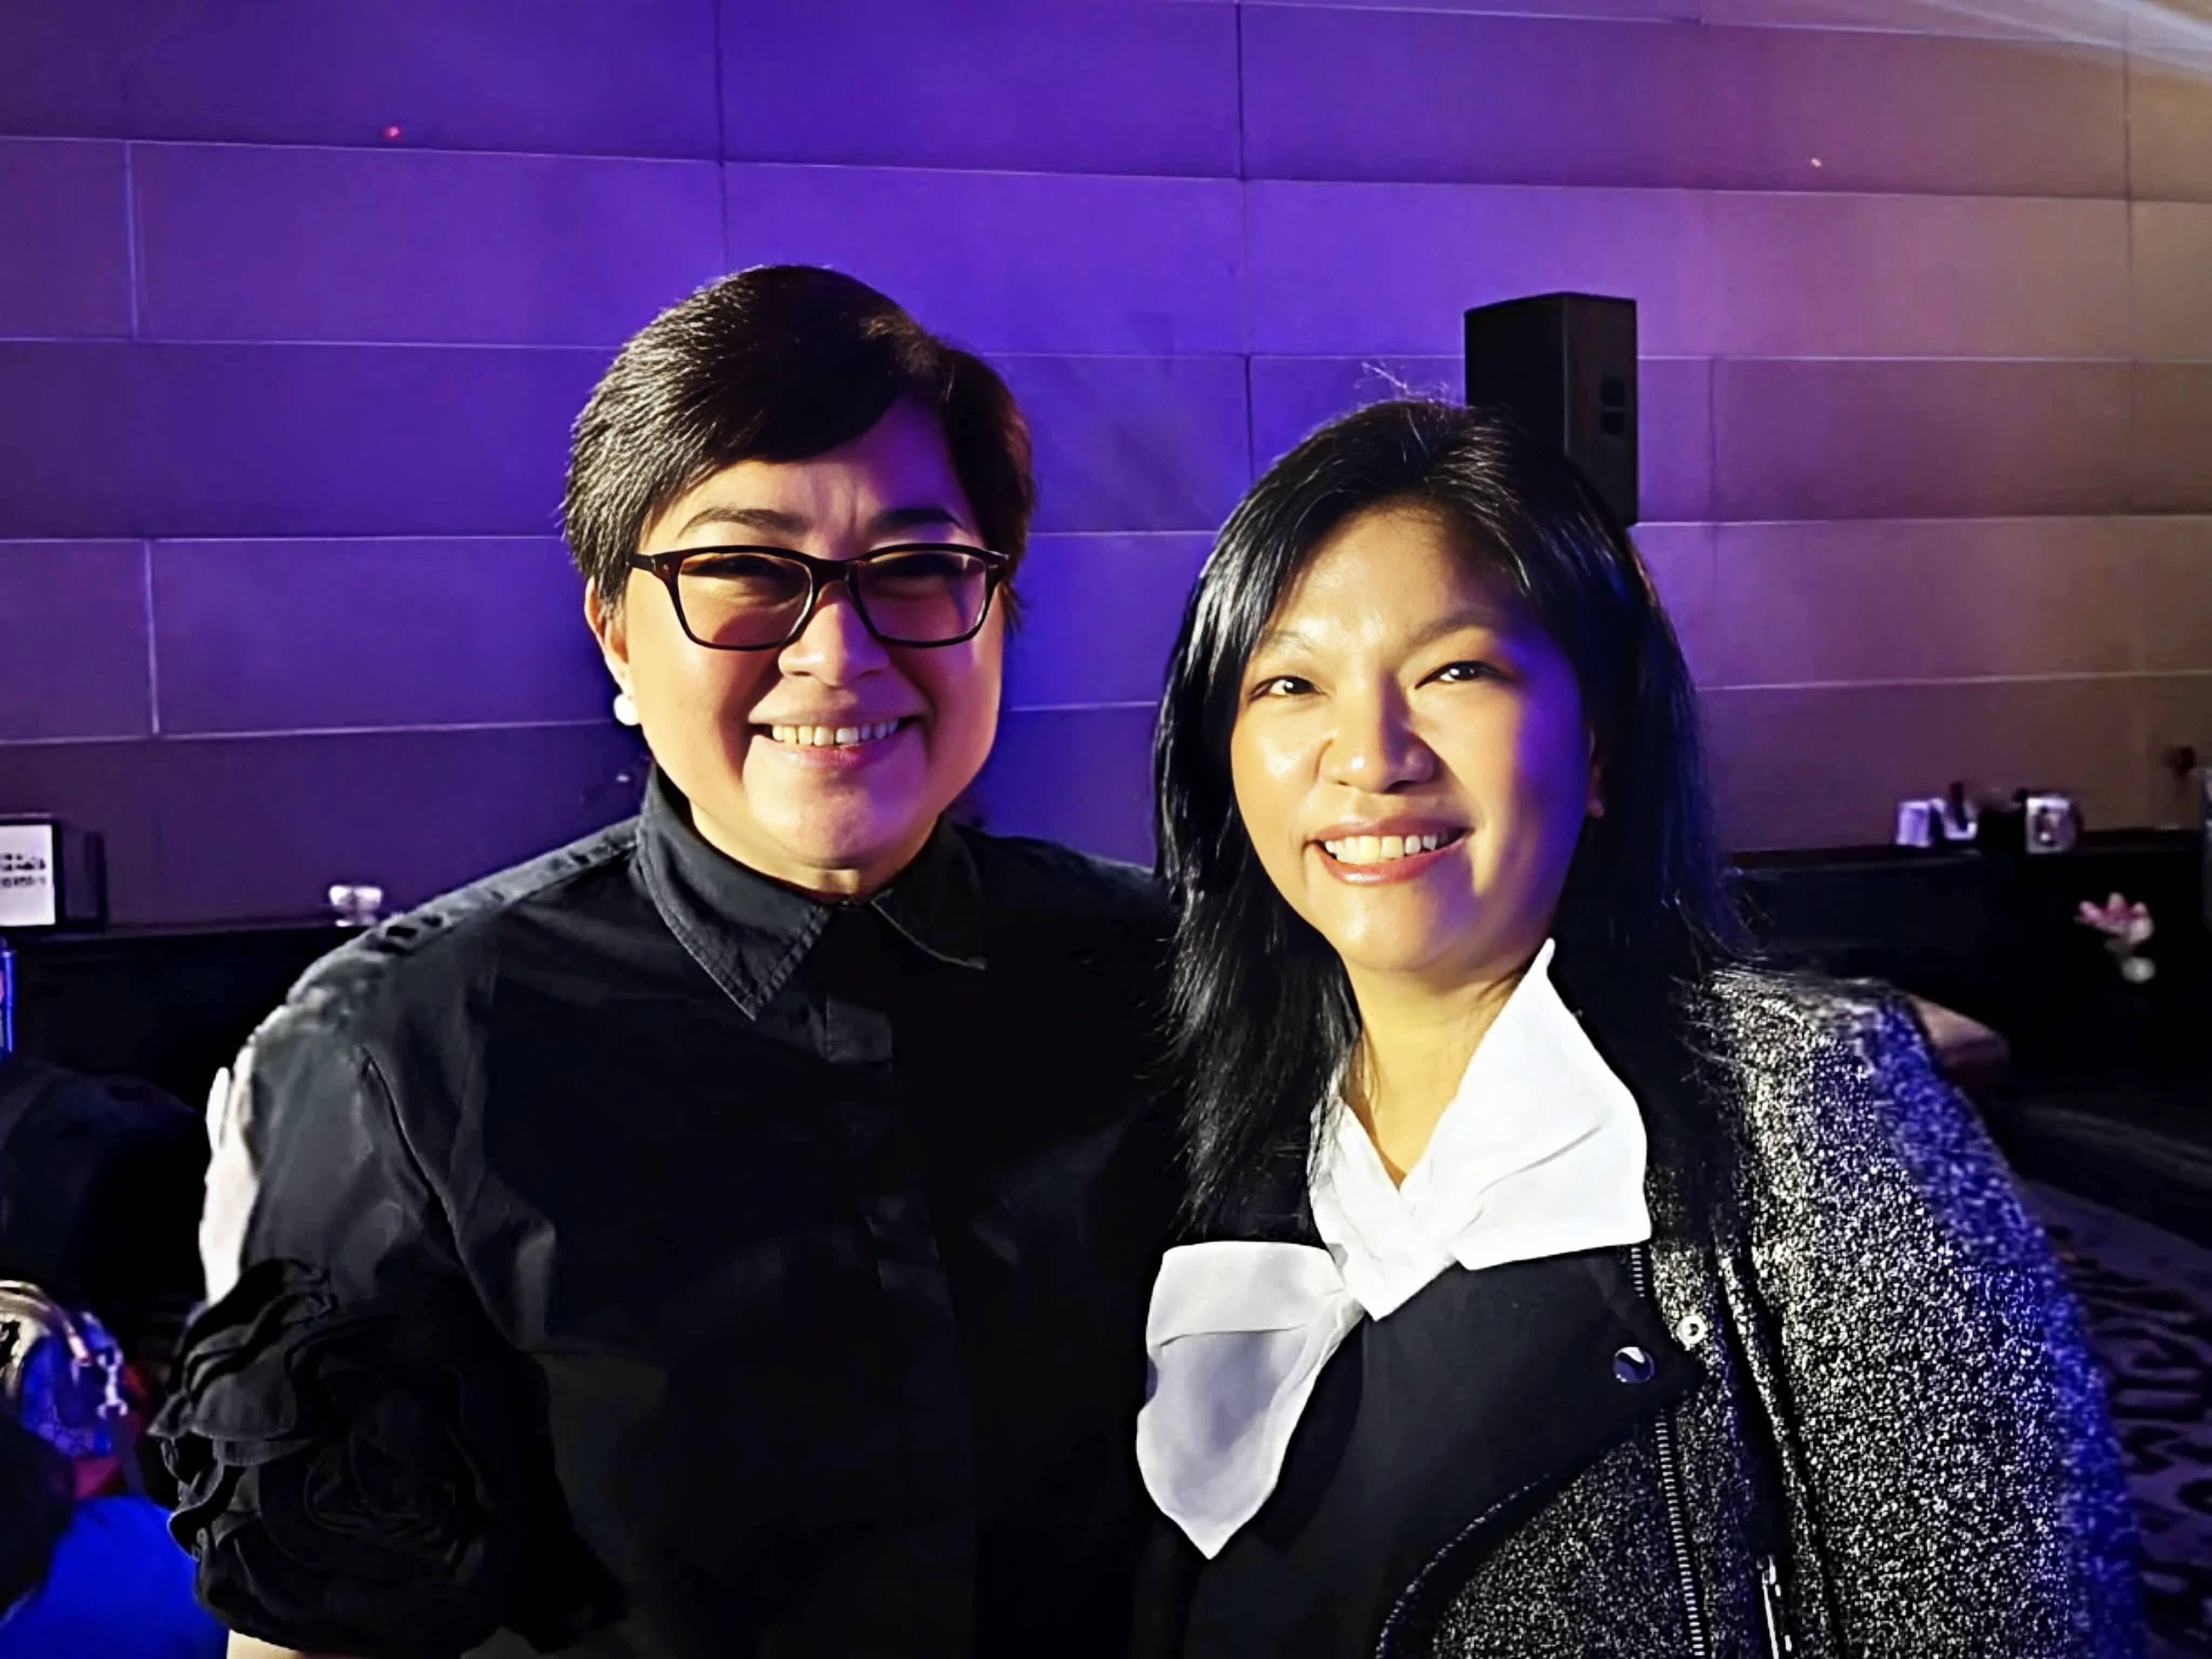
Her career has taken her through digital, media, brand strategy, customer value management, data privacy, and enterprise risk. That non-linear path has allowed her to view privacy through several lenses—not only law and technology, but also customer experience, corporate reputation, human behavior, and trust.
The defining realization came from seeing how deeply telecommunications is woven into everyday life.
"Customer data is one of the most intimate connections between a company and the people it serves."
Telecommunications networks carry people's conversations, relationships, livelihoods, financial transactions, and access to essential services. For Besa-Jimenez, privacy is therefore inseparable from the responsibility of protecting those connections that can change lives.
"As our society accelerates its digital journey, our standards for safety, empathy, and respect must advance just as quickly. It is part of how we fulfill our responsibility to the people whose lives pass through our network every day."
One of the clearest tests of that responsibility came with the implementation of the SIM Registration Act. The initiative required significant changes to platforms, processes, and customer journeys within prescribed timelines while verifying the identities of tens of millions of subscribers. At the same time, PLDT had to introduce new technologies and processes while minimizing vulnerabilities and safeguarding personal data.
For Besa-Jimenez, the experience demonstrated that institutional resilience cannot be separated from privacy.
"The greatest complexity in telecommunications is not scale alone. It is managing enormous scale while executing rapid, organization-wide change."
More importantly, the experience reinforced a principle that continues to guide her approach.
"Privacy cannot be applied as an after-the-fact filter. Institutional resilience comes from integrating governance, privacy, cybersecurity, and risk management from the beginning."
When data protection becomes part of an organization's design DNA, she explains, an enterprise can remain agile and secure even under intense operational and regulatory pressure.
That philosophy also shapes how she approaches the broader organizational challenge of moving privacy beyond compliance.
"We shifted the conversation from compliance to trust."
Compliance may satisfy a regulator, but privacy, she argues, must ultimately honor the trust that customers place in an organization. Behind every data point, billing record, or location log is a human being whose safety, dignity, and autonomy may depend on how responsibly that information is handled.
PLDT reinforced this perspective through its Privacy with PUSO program: Protect, Unite, Stewardship, and Openness. The program translates privacy from an abstract legal obligation into values that people across the organization can understand and practice.
"When product developers, network engineers, customer-care teams, and front-line store personnel see that protecting data also protects people and preserves customer confidence, privacy stops being an administrative requirement. It becomes a source of professional pride and an expression of genuine malasakit."
For an organization as large and varied as PLDT, however, privacy cannot remain the sole responsibility of a central office.
"Privacy is centrally governed but operationally owned."
PLDT, she recounts, has moved away from a purely centralized, top-down enforcement model toward operational accountability. The central Data Privacy Office establishes policy, develops tools and standards, monitors compliance, and provides strategic advice. The business units that collect, use, and manage data, meanwhile, own the privacy risks within their respective domains.
Privacy capability has been embedded into business operations, information technology, customer care, marketing, and other functions. Privacy Impact Assessments are integrated into project gateways, while mandatory training ensures that employees at every level understand their responsibilities.
"This strengthens accountability without fragmenting governance. The central office provides consistency and oversight; operational leaders ensure that privacy is practiced in daily decisions."
That responsibility extends beyond the company's direct customer relationships. In telecommunications, a phone call or message can involve people whose data passes through a network even though they are not subscribers.
"Our responsibility to protect personal data does not begin or end with a customer contract."
If information is processed, she explains, it is protected through clear purpose limitations, appropriate security and confidentiality controls, restricted access, proportionate retention, and Privacy by Design at the infrastructure level.
"We apply strong safeguards consistently across our systems, we protect the confidentiality and integrity of communications involving subscribers and non-subscribers alike."
Her conclusion is simple but far-reaching:
"Privacy protection follows the data—and the person behind it—not merely the contractual relationship."
As emerging technologies continue to reshape telecommunications, the challenge becomes even more complex. Generative AI, IoT, and edge computing are constantly changing the boundaries of data processing, requiring privacy governance to remain agile without compromising customer safety.
An effective Privacy by Design framework, she maintains, must be "principles-based, risk-sensitive, and embedded in the innovation process."
Technology changes quickly, but the core principles of privacy remain remarkably stable: transparency, data minimization, purpose limitation, security, fairness, and accountability. These principles provide the anchors against which new technologies can be evaluated, even when specific use cases or risks have not yet been contemplated by regulation.
The framework must also be proportionate. Higher-risk applications involving sensitive personal data, automated decision-making, large-scale profiling, or vulnerable groups require deeper assessment, stronger controls, and continuing human oversight.
Most importantly, privacy review cannot be left until the end.
"Privacy review must happen early and repeatedly, not as a single approval at the end."
This requires active governance from multidisciplinary teams spanning privacy, cybersecurity, risk, technology, legal, and business functions, allowing concerns to be identified while products and systems can still be redesigned.
"This allows us to innovate at speed without treating customer safety as the price of progress. We can move quickly—but we must move responsibly."
For Data Protection Officers navigating complex enterprises, earning influence, in her view, requires more than knowing privacy regulations.
"To earn a seat at the table, a DPO must speak the language of the business—not only the language of regulation."
A DPO must understand how the enterprise creates value: its operations, customers, technologies, revenue model, and strategic priorities. This is why she considers operational experience particularly valuable, regardless of whether a DPO comes from Operations, Legal, Technology, or Compliance.
The DPO must also present privacy as an enabler of responsible innovation and customer trust, rather than simply a list of restrictions.
"The most effective DPO does not merely say no. The DPO helps the organization determine how to achieve its objective safely and lawfully."
Strategic influence is also earned by translating privacy risk into enterprise impact. Proactive controls protect brand equity, customer loyalty, operational continuity, and long-term enterprise value while helping prevent costly remediation and business disruption.
"Strategic influence is earned when leadership recognizes that the DPO is not there only to interpret the law, but to help the organization make better decisions."
PLDT's privacy journey, she suggests, reflects a broader regional reality: digital transformation cannot succeed without a corresponding transformation in governance and trust.
"As we continuously transform, we also strengthen governance, cyber resilience, and privacy alongside innovation. The more connected the digital economy becomes, the more trust becomes essential infrastructure. Privacy is one of its foundations."
That infrastructure cannot be built by any single company or jurisdiction. Data and digital services move across organizations and national borders, while regulatory regimes remain at different stages of maturity. Government and industry therefore need to work together to align standards, enable secure and lawful data interoperability, exchange information, and develop effective cross-border enforcement mechanisms.
"The larger lesson is that regional digital growth and regional trust must advance together."
For business leaders and professionals who still see privacy primarily as a legal or cost function, there is another way to understand its value.
"Treating data protection purely as a regulatory cost means overlooking one of its greatest strategic benefits: Trust."
In a digital-first economy, customers are not merely buying a product or service. They are entrusting an organization with parts of their identity, behavior, relationships, and daily life. Organizations that handle that trust well strengthen customer loyalty, protect brand equity, and gain the confidence to innovate responsibly.
Good privacy governance also creates operational value. It improves data quality, clarifies accountability, reduces unnecessary data collection, strengthens security, and lowers the likelihood of costly incidents and business disruption.
Privacy requires investment, she acknowledges. But the more important question is not simply what privacy costs.
"What does the absence of trust cost the enterprise?"
When privacy is treated as a core trust asset, risk management becomes a source of resilience—and ultimately, competitive advantage.
The Cyber Woman of the Year title, awarded at the PhilSec 2026 Awards, also highlights another dimension of her leadership: the ability to bring together disciplines that have traditionally operated separately. She has led data privacy for PLDT Group since 2017 and has held the Enterprise Risk mandate alongside it since 2021—a span in which she has had to make the two functions work as one.
Her own career has taken her through brand strategy, digital, media, customer relationship management, data privacy, and enterprise risk.
"It's not a conventional path, but together they gave me the multidimensional perspective required to lead in a field where technology, governance, people, and business constantly intersect."
For young women entering technology and cybersecurity, she encourages them to question the assumptions others make about what women can do—and, just as importantly, the assumptions they may have absorbed about themselves.
"You do not need to imitate a traditional model of leadership to succeed. Develop real expertise. Understand the business. Remain curious. Exercise courage when the stakes are high. And retain your humanity."
Her message extends beyond gender. It is a call to recognize that leadership does not require fitting a predetermined profile.
"Impact comes not from fitting the expected profile, but from bringing the full depth of your experience to the work."
As APDPO continues its mission to elevate privacy leadership and collaboration across the Asia-Pacific region, cooperation, she stresses, is essential to addressing the challenges ahead.
"My message is simple: let us work together."
AI governance, sophisticated cyber threats, cross-border data flows, and regulatory alignment now sit squarely in that shared territory.
"Networks such as APDPO give us a vital platform to exchange experience, develop stronger and more consistent standards, connect policy with operational reality, and mentor the next generation of privacy leaders," she says.
But collaboration must extend beyond dialogue.
"We must build practical bridges between government and industry, between regulation and innovation, and between national priorities and regional cooperation."
At the center of that work remains a simple principle:
"Behind every system, transaction, and data point is a human being."
By pushing privacy ownership out into the business rather than keeping it inside a central office, Besa-Jimenez is asking a telecom the size of PLDT to move at the speed AI, IoT, and edge computing now demand while keeping privacy a responsibility every operational leader carries, not one they defer upward. That kind of model depends on operational leaders continuing to treat privacy risk as their own well after the initial mandate has become routine. Her repeated return to a single image, the human being behind the data point, points to how she hopes that continues: as habit of mind rather than policy language. As automated decision-making moves deeper into how PLDT serves its customers, that habit will continue to be tested—and how it holds will say much about whether this transformation was built to last.
APDPO thanks Leah Besa-Jimenez for sharing her insights, Magie Antonio, APDPO Country Head for the Philippines, for the conversation on privacy leadership, and the PLDT Group for its support in advancing the dialogue on data privacy, trust, and responsible innovation.